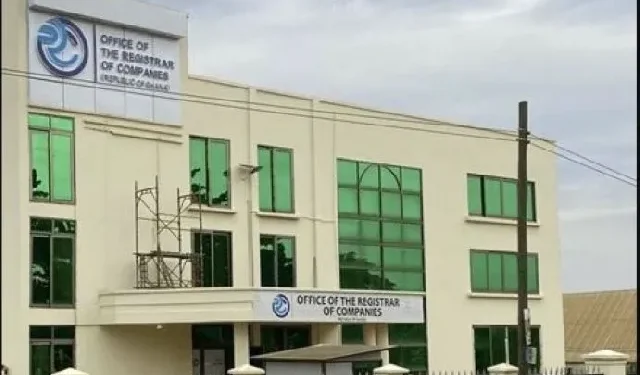
The Cyber Security Authority (CSA) has imposed fines totaling GH¢360,000 on the Office of the Registrar of Companies (ORC) and Purpleline Solutions Limited for violating provisions of Ghana’s Cybersecurity Act, 2020 (Act 1038).
The sanctions were issued after the Authority found that the ORC engaged an unlicensed cybersecurity service provider despite specific directives requiring it to use a licensed provider.
The ORC, which is designated as a Critical Information Infrastructure (CII) institution, was fined GH¢240,000 for failing to comply with two directives issued by the CSA. Purpleline Solutions Limited was separately fined GH¢120,000 for providing cybersecurity services without the required license.
According to the CSA, it instructed the ORC on June 15, 2026, to engage only Tier 1 licensed Cybersecurity Service Providers (CSPs) to enhance the security and resilience of its critical systems.
The ORC was also directed to submit details of its cybersecurity service providers, the Terms of Reference for its proposed Security Operations Centre (SOC), and relevant approvals from the Public Procurement Authority.
However, the Authority said the ORC proceeded to engage Purpleline Solutions Limited, which was not licensed by the CSA to provide regulated cybersecurity services.
The Authority determined that the ORC failed to comply with two separate directives and imposed a fine of 10,000 penalty units for each breach, bringing the total penalty to GH¢240,000. It has also ordered the ORC to comply with the outstanding directives within one month.
Purpleline Solutions Limited was sanctioned after the CSA concluded that it had provided cybersecurity services without first obtaining the required license.
The Authority noted that although Purpleline applied for a cybersecurity service provider license on July 15, 2026, the application was submitted after it had already been engaged by the ORC.
The CSA stressed that submitting a license application does not permit a company to begin regulated cybersecurity operations.
The Authority used the case to issue a broader warning to public institutions and private companies involved in cybersecurity services.
It cautioned organisations against awarding contracts to unlicensed providers and warned service providers that they must obtain the appropriate license before offering regulated cybersecurity services.
The CSA also directed designated Critical Information Infrastructure institutions and other entities covered by the Cybersecurity Act to verify both the licensing status and the appropriate license tier of cybersecurity service providers before engaging them.
The Authority said it would continue to monitor compliance and take enforcement action against institutions that engage unlicensed providers and companies that operate without the necessary licenses.
“Cybersecurity licensing is a legal requirement, not an administrative formality,” the CSA stated, adding that it will continue to use its regulatory powers to ensure organisations responsible for critical systems and sensitive information comply with Ghana’s cybersecurity laws.